The U.S. Army Engineering and Support Centre in Huntsville says it has completed the first phase of a multi-year effort to catalogue and assess operational technology, a step the service describes as essential to managing cyber risk in facilities that increasingly connect industrial-control systems to enterprise networks.
From discovery to remediation
The Huntsville Centre’s project began in fiscal 2021 with inventory contracts covering the Army Reserve and later expanded to include the Army National Guard and the Defense Logistics Agency. Officials say inventories for the Reserve are now complete and that final deliverables for the Logistics Agency are being delivered, while National Guard work continues.
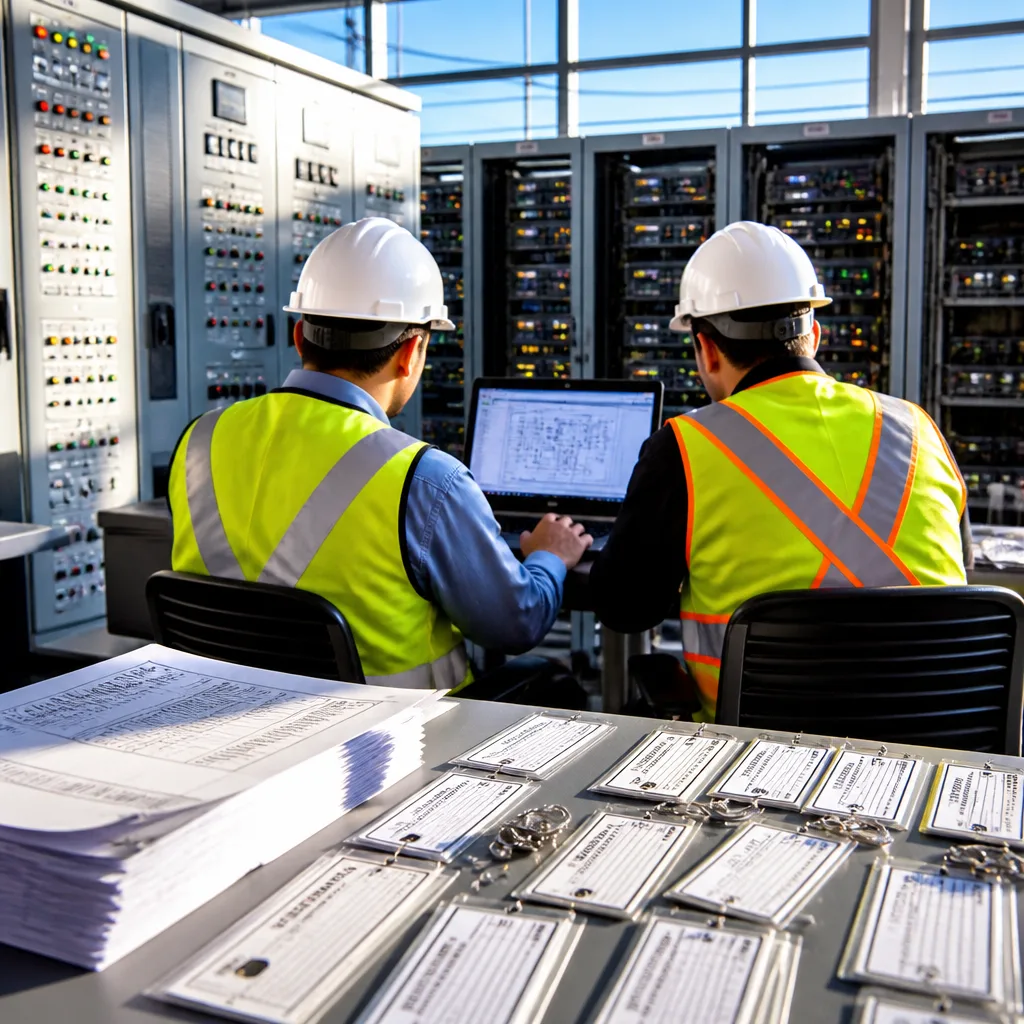
Operational technology, or OT, encompasses the hardware and software that monitor and control building systems and other facility equipment — examples cited by the centre include heating, ventilation and air-conditioning systems, fire detection, access control and surveillance cameras, building-management systems and some medical devices. Within the Defence context, many such systems are categorised as facility-related control systems (FRCS).
"Operational technology is no longer isolated infrastructure. These systems have digital identities, communicate across networks and directly support critical missions," said Kevin Miller, Huntsville Centre Operational Technology Branch project manager. "Before organisations can secure them, they have to know exactly what they own, where it is and what risks it presents."
The inventories complete the project’s initial stage of asset identification and inventory compilation. The programme will now shift emphasis toward developing remediation strategies and plans for long-term sustainment — work intended to help military leaders decide where to invest and how to sequence modernization to reduce cyber exposure.
Why the inventory matters
OT devices historically sat on isolated networks and were managed by engineering rather than IT teams. As those devices gain network connectivity to enable remote monitoring, automation and data gathering, they inherit many of the same vulnerabilities that affect enterprise IT — from weak authentication to unpatched software and unsupported legacy components.
For defence organisations, compromised OT can have consequences well beyond data theft: degraded environmental controls, disabled fire suppression, or corrupted access systems can disrupt operations and put personnel or materiel at risk. The Huntsville Centre frames the inventory as a prerequisite to more precise risk management because you cannot protect what you do not know you have.
- Scope: Inventories started in FY2021 for the Army Reserve; National Guard work awarded through 2024; DLA deliverables nearing completion.
- Focus shift: From asset discovery to remediation planning and sustainment.
- OT examples: HVAC, fire alarms, access control, surveillance, building management, medical equipment.
The programme constructs a baseline that commanders and infrastructure managers can use to prioritise upgrades, patching programmes, network segmentation and procurement decisions. That prioritisation is especially important where budgets are constrained and not all systems can be hardened immediately.
Broader implications and challenges
The Huntsville Centre’s activity mirrors a wider recognition across governments and industry that OT must be integrated into cybersecurity frameworks. However, turning inventories into action is a complex task.
Challenges include coordinating across multiple tenants and owners inside the Department of Defense, reconciling engineering and IT responsibilities, and funding the remediation work. Many OT devices have long lifecycles and were not designed with security updates in mind; replacing or retrofitting them can be costly and operationally disruptive.
Additionally, inventories are only as useful as the governance and processes built around them. Sustained benefit requires regular updates, change-control integration and the allocation of resources so remediation does not stall after the initial reporting phase.
For allied and partner forces watching the U.S. effort, the Huntsville Centre’s approach may offer a model: start with comprehensive discovery, then move to risk-based remediation. Provided the next phase — funding and executing mitigation plans — follows through, the inventories could materially reduce OT attack surface across thousands of facilities that support critical missions.
The Huntsville Centre did not release detailed findings such as counts of devices or specific vulnerabilities in its public statement. It framed the milestone as a turning point: the move from cataloguing to acting on risk.
Whether that promise translates into measurable reductions in operational cyber risk will depend on interagency cooperation, procurement choices and the sustained attention of military leadership as remediation plans are implemented.